BEST WISHES FROM
Balasubramanian Swaminathan
While the Indian Government is busy protecting the citizens from multiple online scams including digital arrest, voice-based scams, the increasing attacks on the enterprises are sky-rocketing. India has faced significant ransomware challenges with over 340 victim organizations reported as targets by multiple ransomware groups, according to the latest data from ransomware.live. This indicates a growing threat landscape in the country with at least 73 distinct ransomware groups active against Indian entities.
Some of the most prominent attacks in India in the recent days which are reported include Star Health, Aditya Birla Capital Digital (ABCD) App, Sant Parmanand Hospital (Delhi), NKS Super Specialty Hospital (Delhi), Kolkata Police Cyber Crime Wing, Nippon Life India Asset Management (NAM India) and Central Bank of India. Even though Indian victims cover various industries, predominant are from the BFSI (banking and financial services industries) and healthcare reflecting how cybercriminals exploit vulnerabilities across critical infrastructure and businesses in the country.
What is worrisome is that some high-profile ransomware cases in India have involved demanding multimillion-dollar ransoms, with significant financial and operational disruption to targeted organizations. This surge in ransomware incidents corresponds with India’s massive digital transformation drive, expanding internet user base, and growing adoption of digital services.
Lack of regulations:
 One major reason for the increasing attacks among the enterprises in India is the lack of ownerships and responsibilities among them. According to Balaji S of Vyapini Tech Services, there is a common misconception that cyber-attack will result only in ransomware or attack on technology infrastructure. However, he points out the fact that lack of proper cyber-security postures would lead to real-life crimes. “Recently there was a case of organ transplantation rackets happened in India. Many hospitals in India were accused of forcibly operating out the vital parts of an organ including ‘Kidney’ for money. Not many would believe that the data of the potential donors and receivers were accessed through compromised data in hospitals.”, he says. Balaji feels that India being a country with vast population, the analytics and insights that can be extracted from Indian patients are a golden treasure for the global pharma and drug manufacturers. “Even a state will have a population of the country in many aspects. Thus, any data available through an organized or unorganized cyber attacks makes huge difference to drug manufacturers”, Balaji avers.
On the other hand, India’s India’s financial institutions are continually targeted by cyber threats because they store enormous volumes of confidential information, spanning customer financial details and personal identities, alongside vast reserves of monetary wealth, making them extremely appealing to both criminal groups seeking profit and organized state-backed hackers. India is also increasing their spends on non-conventional investment avenues including share trading, mutual funds and the GenZ population even trying their hands dirt on crypto and bit-coins. This is one avenue where hackers play a key game.
The rapid expansion of the nation’s digital transaction infrastructure, exemplified by systems like UPI (unified payment interface), significantly broadens the potential areas of exploitation, multiplying the access points for malicious activity. A core challenge arises from the pressure to adopt digital services quickly, which often necessitates blending older, existing technology platforms with newer cloud-based and financial technology solutions, resulting in complex setups with inherent security weaknesses.
Reason for increasing attacks despite increase in spends:
 Anand V, of Raksha Technologies, one of the leading cyber security solution providers in India calls it lack of monitoring the reason for major attacks. Anand also firmly rejected the myth that attacks are happening only in the BFSI and healthcare sector. “While the perception is different from India, I can firmly say, every industry in India is vulnerable for attacks. One of my customers is from automative sector who faced severe attacks who had tough time recovering from that.” Anand also recalls a major cyber-attack on Jaguar Land Rover (JLR) in late August 2025 caused a shutdown of global production for about a month, with a phased restart beginning in early October. The attack resulted in significant financial losses for the quarter ending in September 2025. The incident, suspected to be the costliest cyber-attack in UK history, also impacted the company’s supply chain and dealers, though JLR states there is no evidence of customer data theft. “Such attacks in an international firm would have snowball effect amongst the suppliers in India as well.
Major Vulnerabilities in both the segments:
“The healthcare and BFSI sectors in India are currently navigating a significant surge in cyberattacks, driven by a perfect storm of digital evolution and systemic vulnerabilities,” says Manasi Saha, Founder of Macaws Infotech.
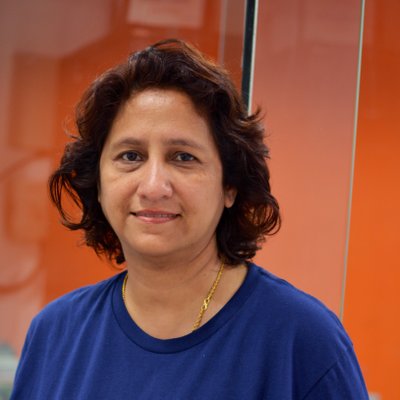
Manasi Saha
“In the healthcare space, we see a dangerous combination of legacy technology and high-value patient data. While the rapid shift toward telemedicine and digital records is a step forward, it has expanded the attack surface for institutions that often lack the specialized cybersecurity expertise to defend it. Essentially, medical data has become a prime currency for cybercriminals.
Similarly, the BFSI sector remains a top-tier target due to the sheer sensitivity of the financial data it manages. As banks and financial institutions undergo rapid digital transformation, they are opening new doors through cloud environments and APIs that—if not properly secured—become easy entry points. We are also seeing much more sophisticated phishing and social engineering tactics designed to exploit the human element.
To stay ahead of these threats, it is no longer optional for organizations to be reactive. They must prioritize robust security protocols, conduct rigorous regular audits, and, perhaps most importantly, invest in continuous employee training to build a culture of cyber-resilience.”
Self-Reliance is must:
While many experts feel that cybersecurity is not just a CISO-work, a holistic approach in creating awareness should happen. As a ray of hope, the mandatory security audit for Micro, Small, and Medium Enterprises (MSMEs) in India is a significant compliance requirement introduced by the Indian Computer Emergency Response Team (CERT-In) to create a basic level of cybersecurity defense across this vital sector. The audit is mandated under the authority granted to CERT-In by Section 70B of the Information Technology (IT) Act, 2000.
Currently all eyes on the Digital Personal Data Protection Act (DPDP Act) which is anticipated to radically alter India’s digital environment. Citizens, referred to as Data Principals, will acquire comprehensive privileges, such as the authority to request their information be deleted or rectified, and to exercise clear control over how their consent is utilized. Corporations, designated as Data Fiduciaries, will be obligated to adopt strict, verifiable security protocols and issue unambiguous privacy statements, ensuring data is processed strictly for the initial reason it was gathered (known as purpose limitation). A specialized regulatory agency, the Data Protection Board (DPB), will supervise adherence to these regulations, thereby establishing digital responsibility as a necessary legal and financial requirement for all businesses active in India.